Everything in one place.
Whitepapers, case studies, datasheets, and videos from across the Kusari team and community.
Welcome to the Island of Misfit Stacks
Why supply chain security breaks on the stacks regulated industries run. Andrew Martin of ControlPlane and Tim Miller of Kusari, live on October 14.
Watch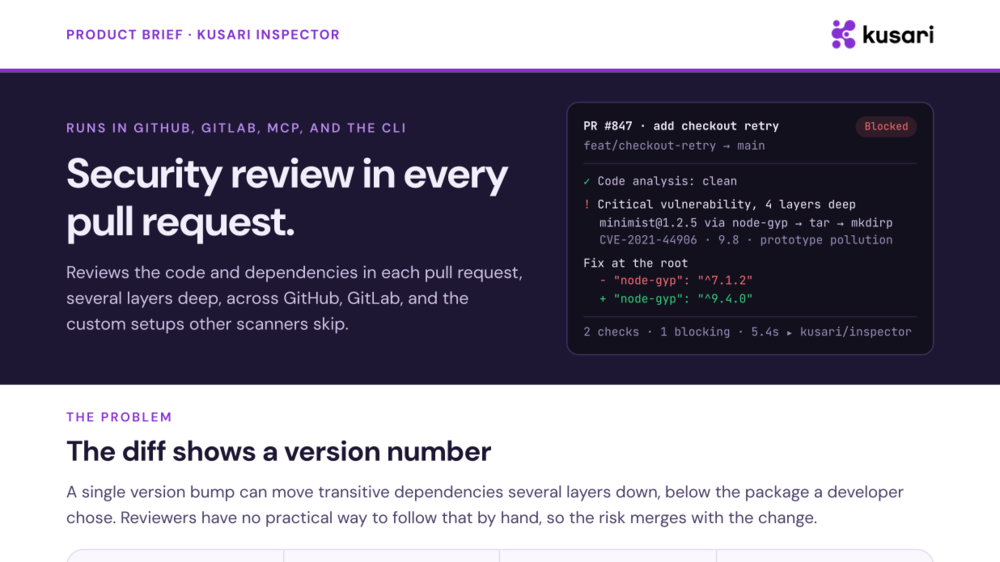
Kusari Inspector: Security review in every pull request
Reviews the code and dependencies in each pull request, several layers deep, across GitHub, GitLab, and the custom setups other scanners skip.
View datasheet
Kusari Platform: Built for the stacks your scanner gave up on
Supply chain security for regulated industries. Kusari builds the dependency graph from your source code, so it runs on the stack you have, no matter how complicated.
View datasheet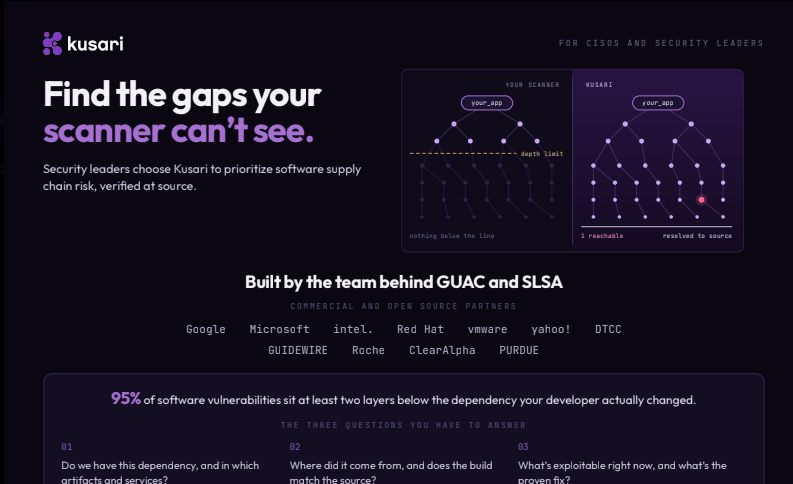
Kusari: Find the gaps your scanner can't see
Security leaders choose Kusari to prioritize software supply chain risk, verified at source.
View datasheet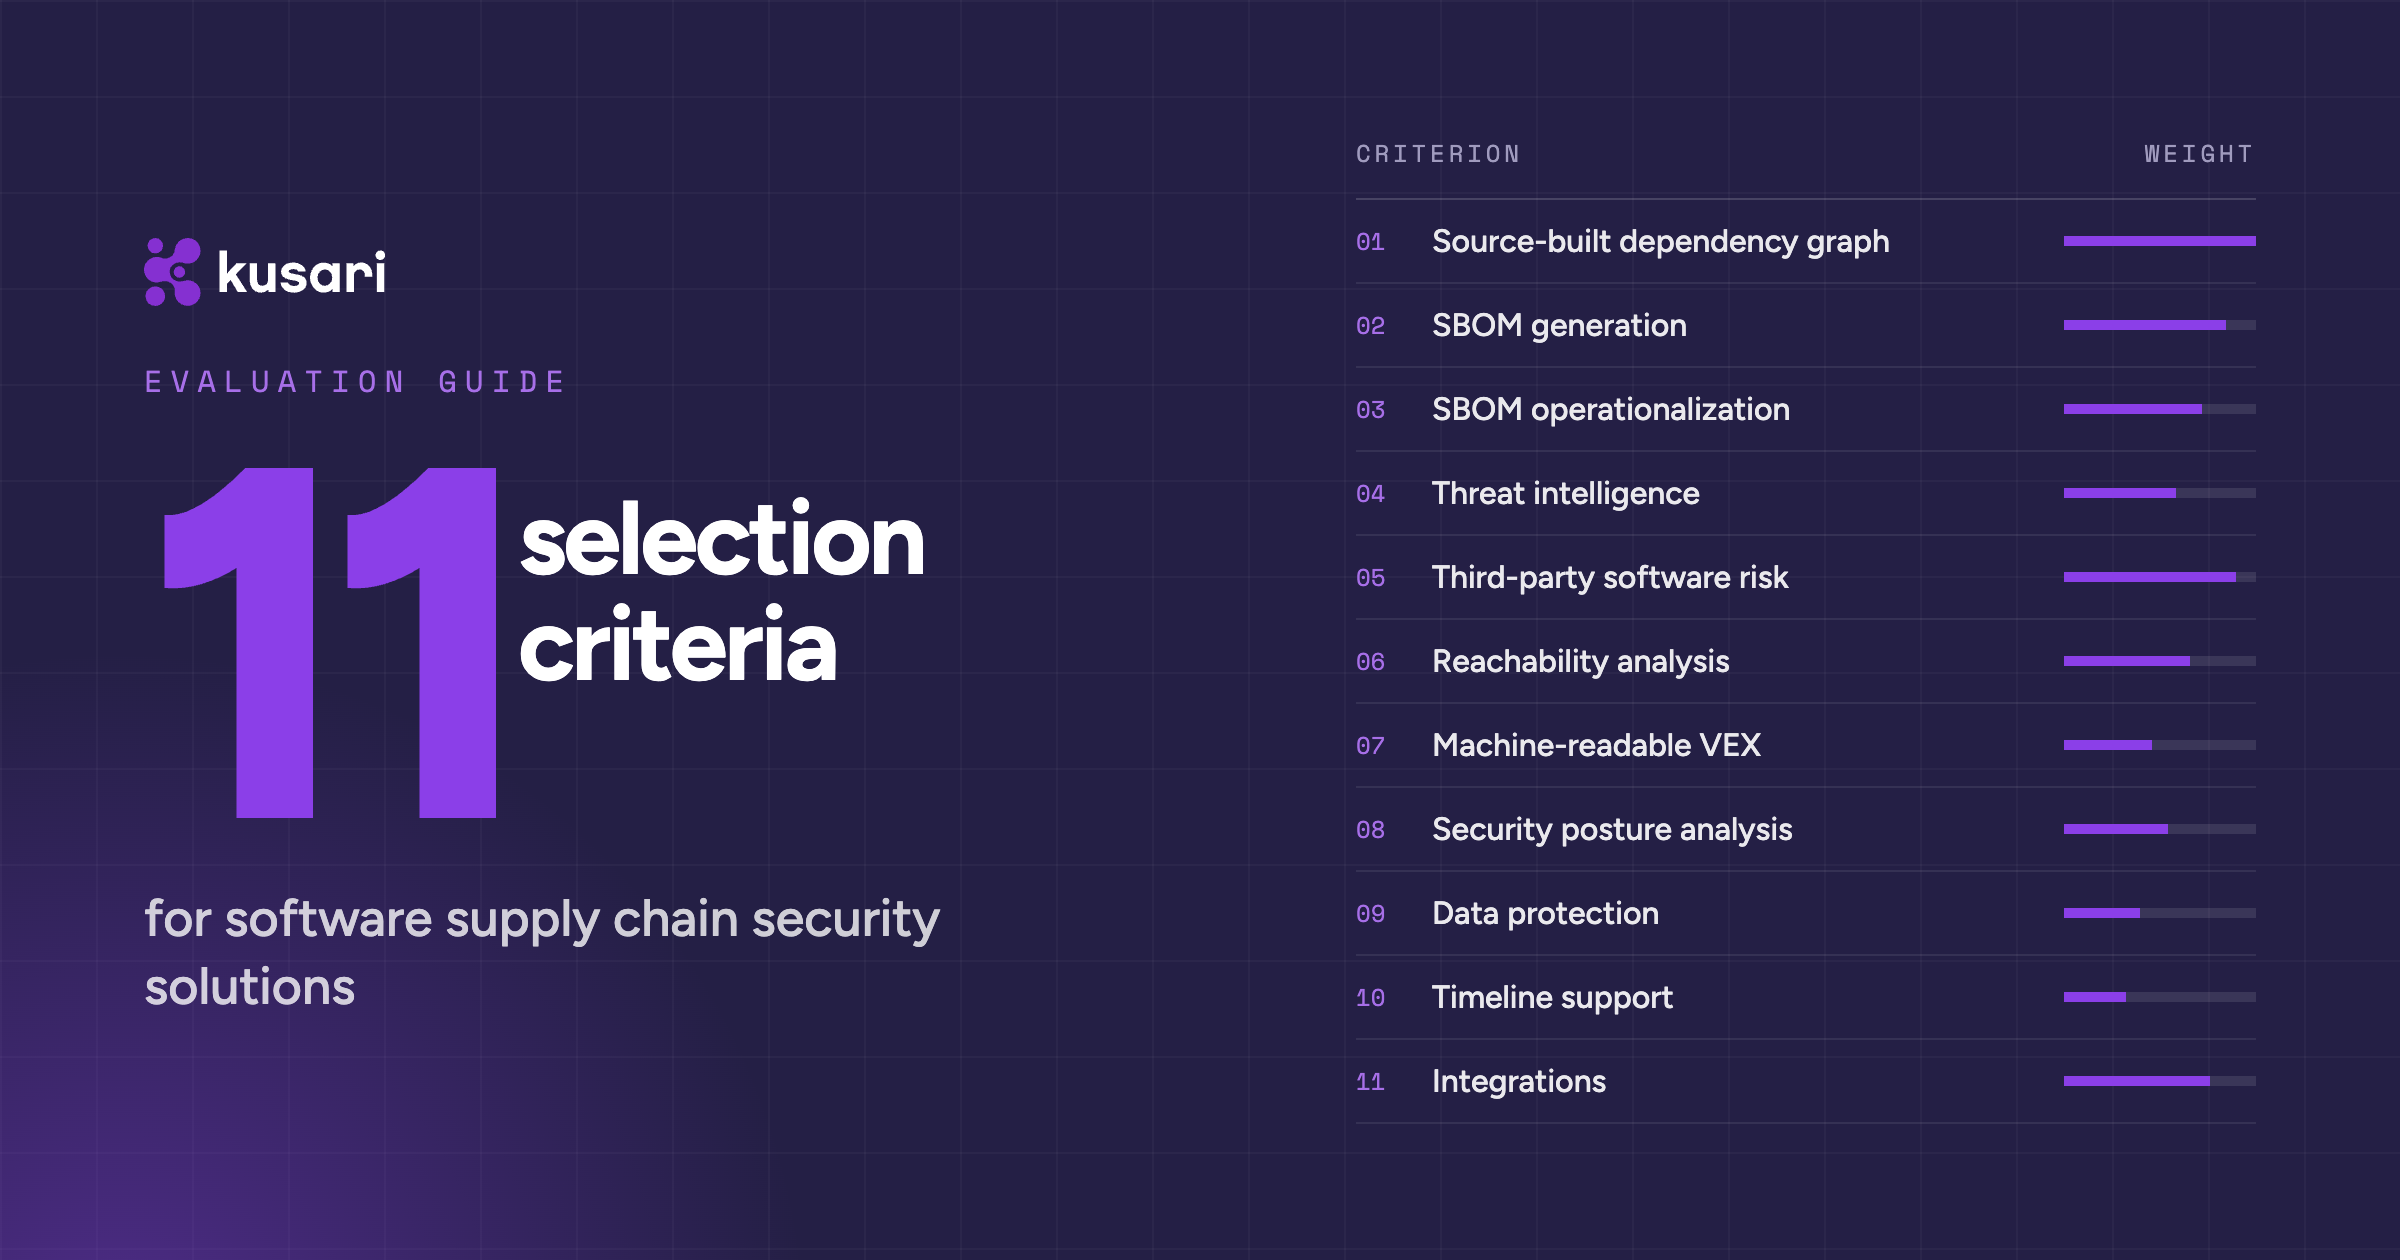
Evaluating Software Supply Chain Security Solutions
11 criteria for evaluating software supply chain security solutions, from SBOM generation and reachability analysis to VEX support and integrations.
Read paper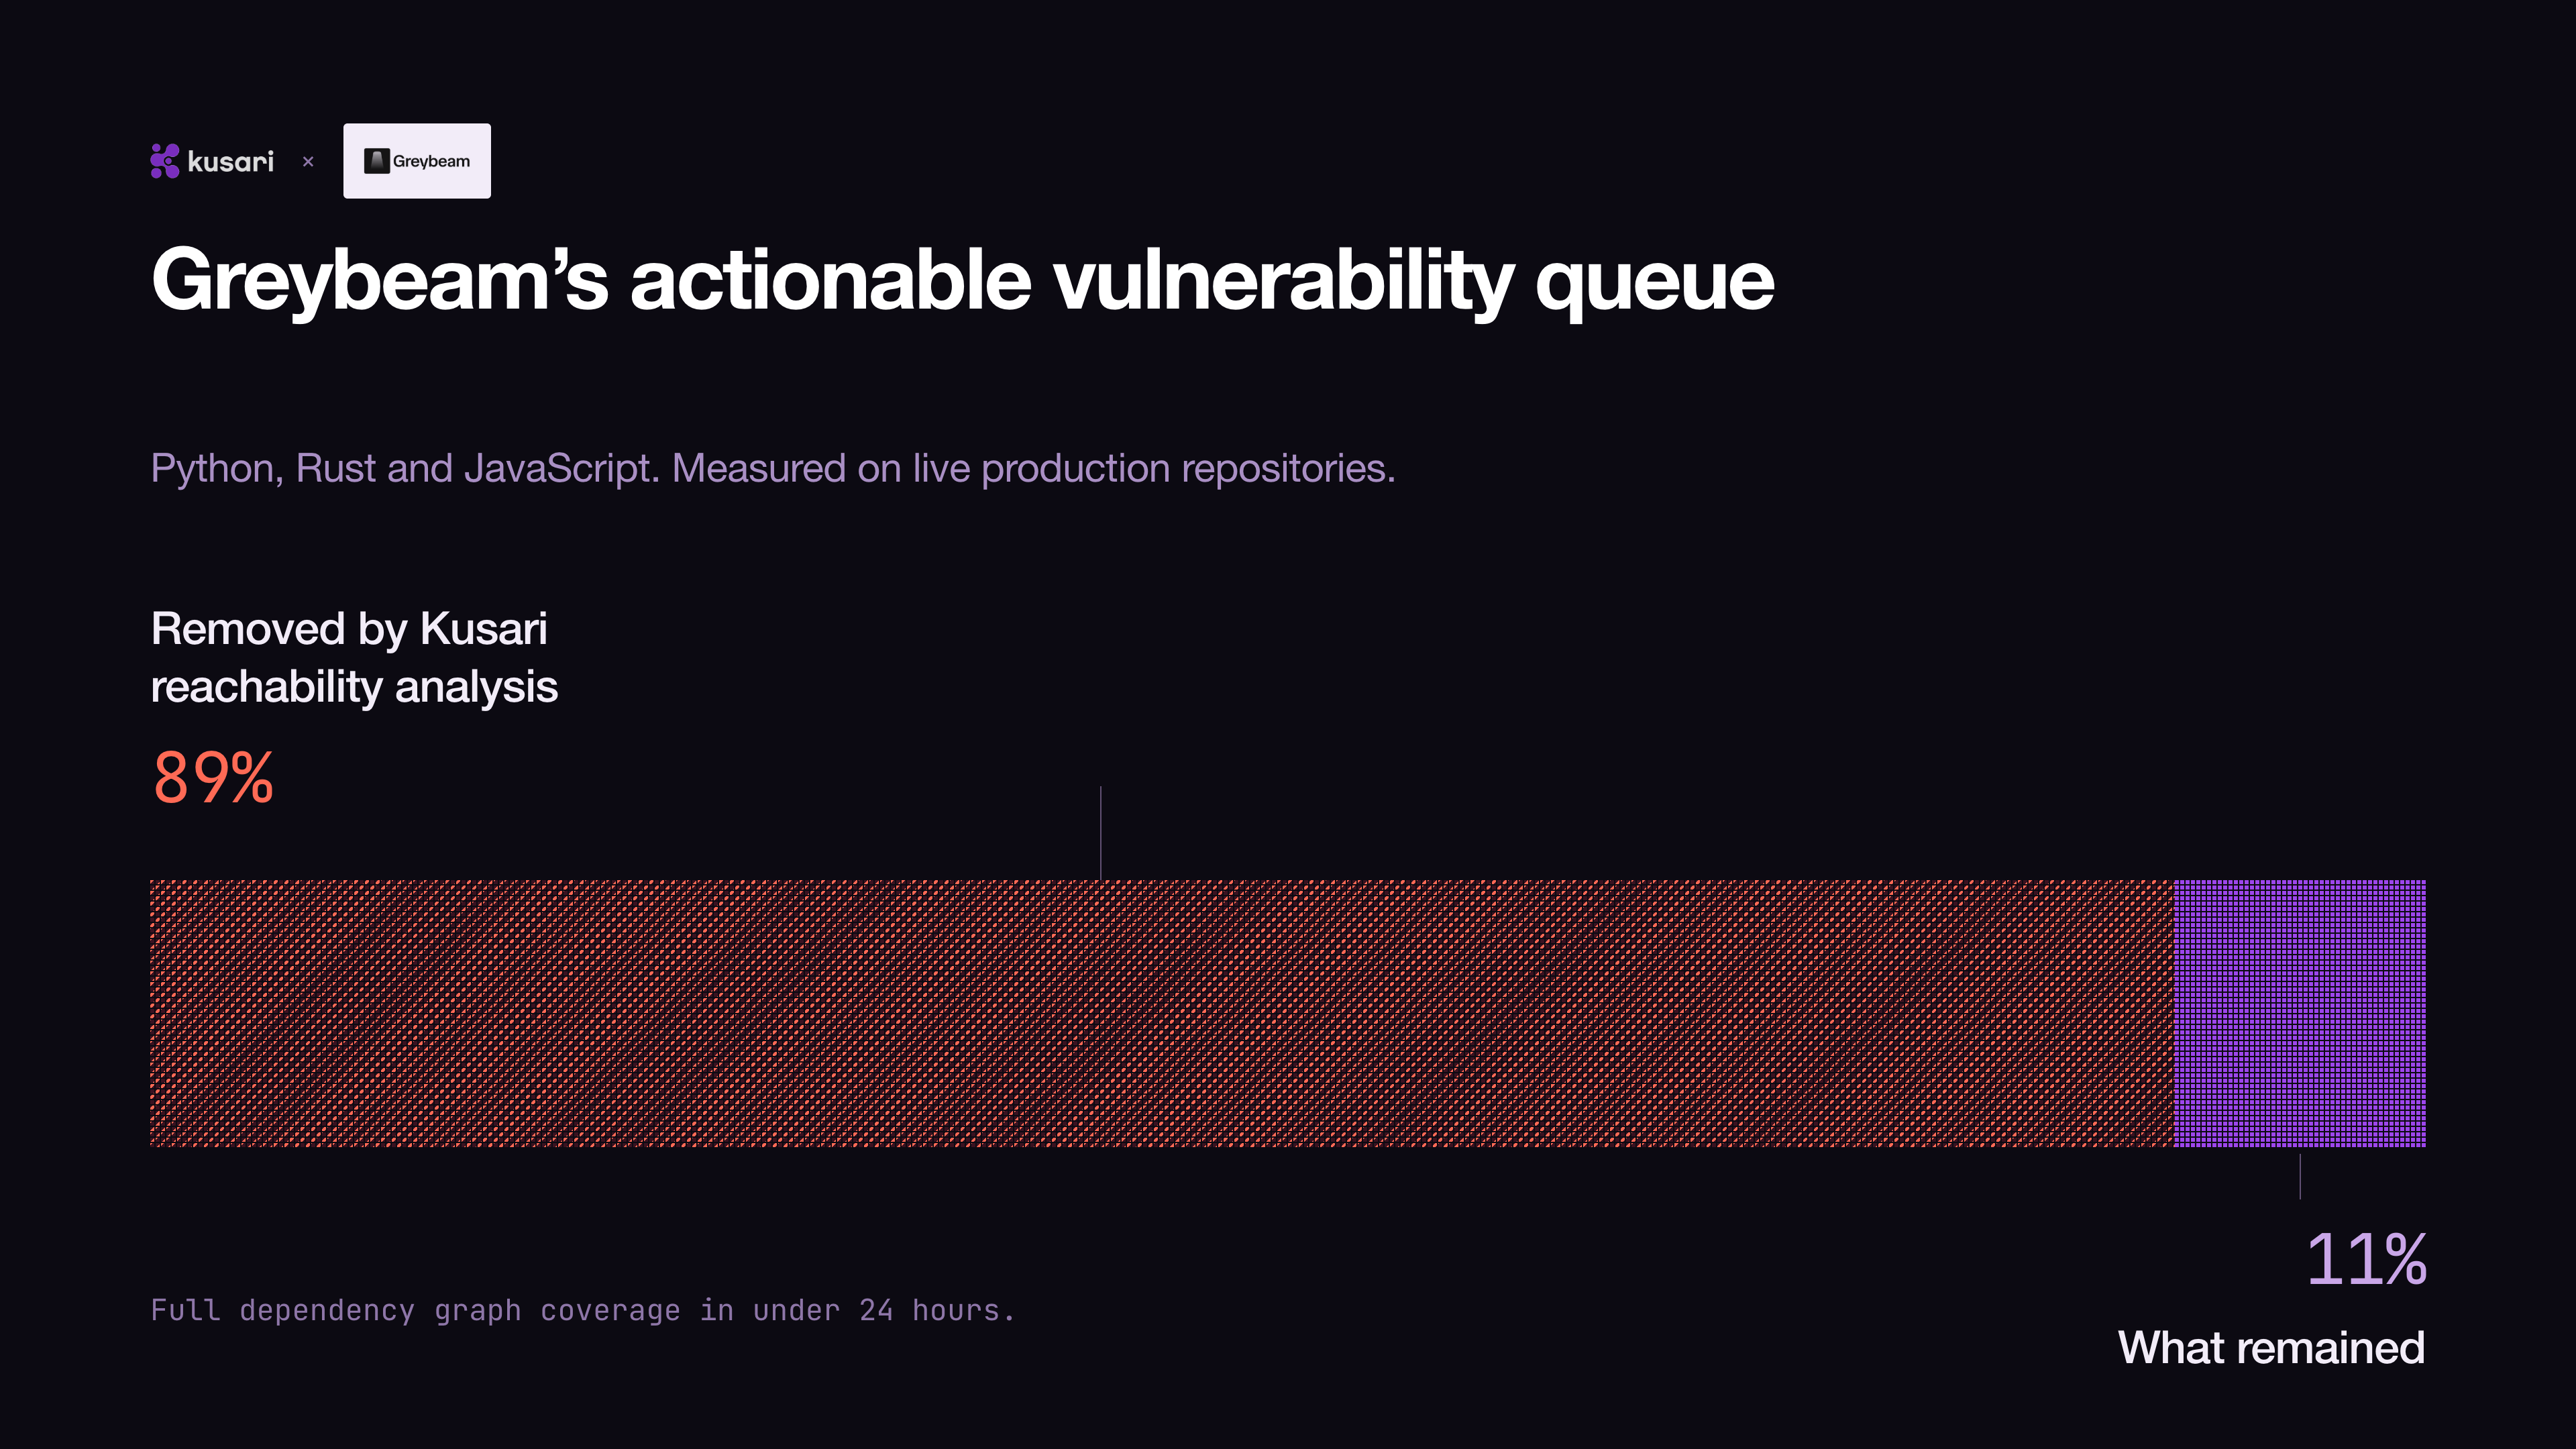
Greybeam Cuts Its Actionable Vulnerability Queue by 89%
Greybeam already trusted Kusari Inspector in its pull requests. Expanding to the full Kusari Platform built the dependency graph on day one and, with reachability analysis layered on top, cut the actionable vulnerability queue by 89%.
Read case study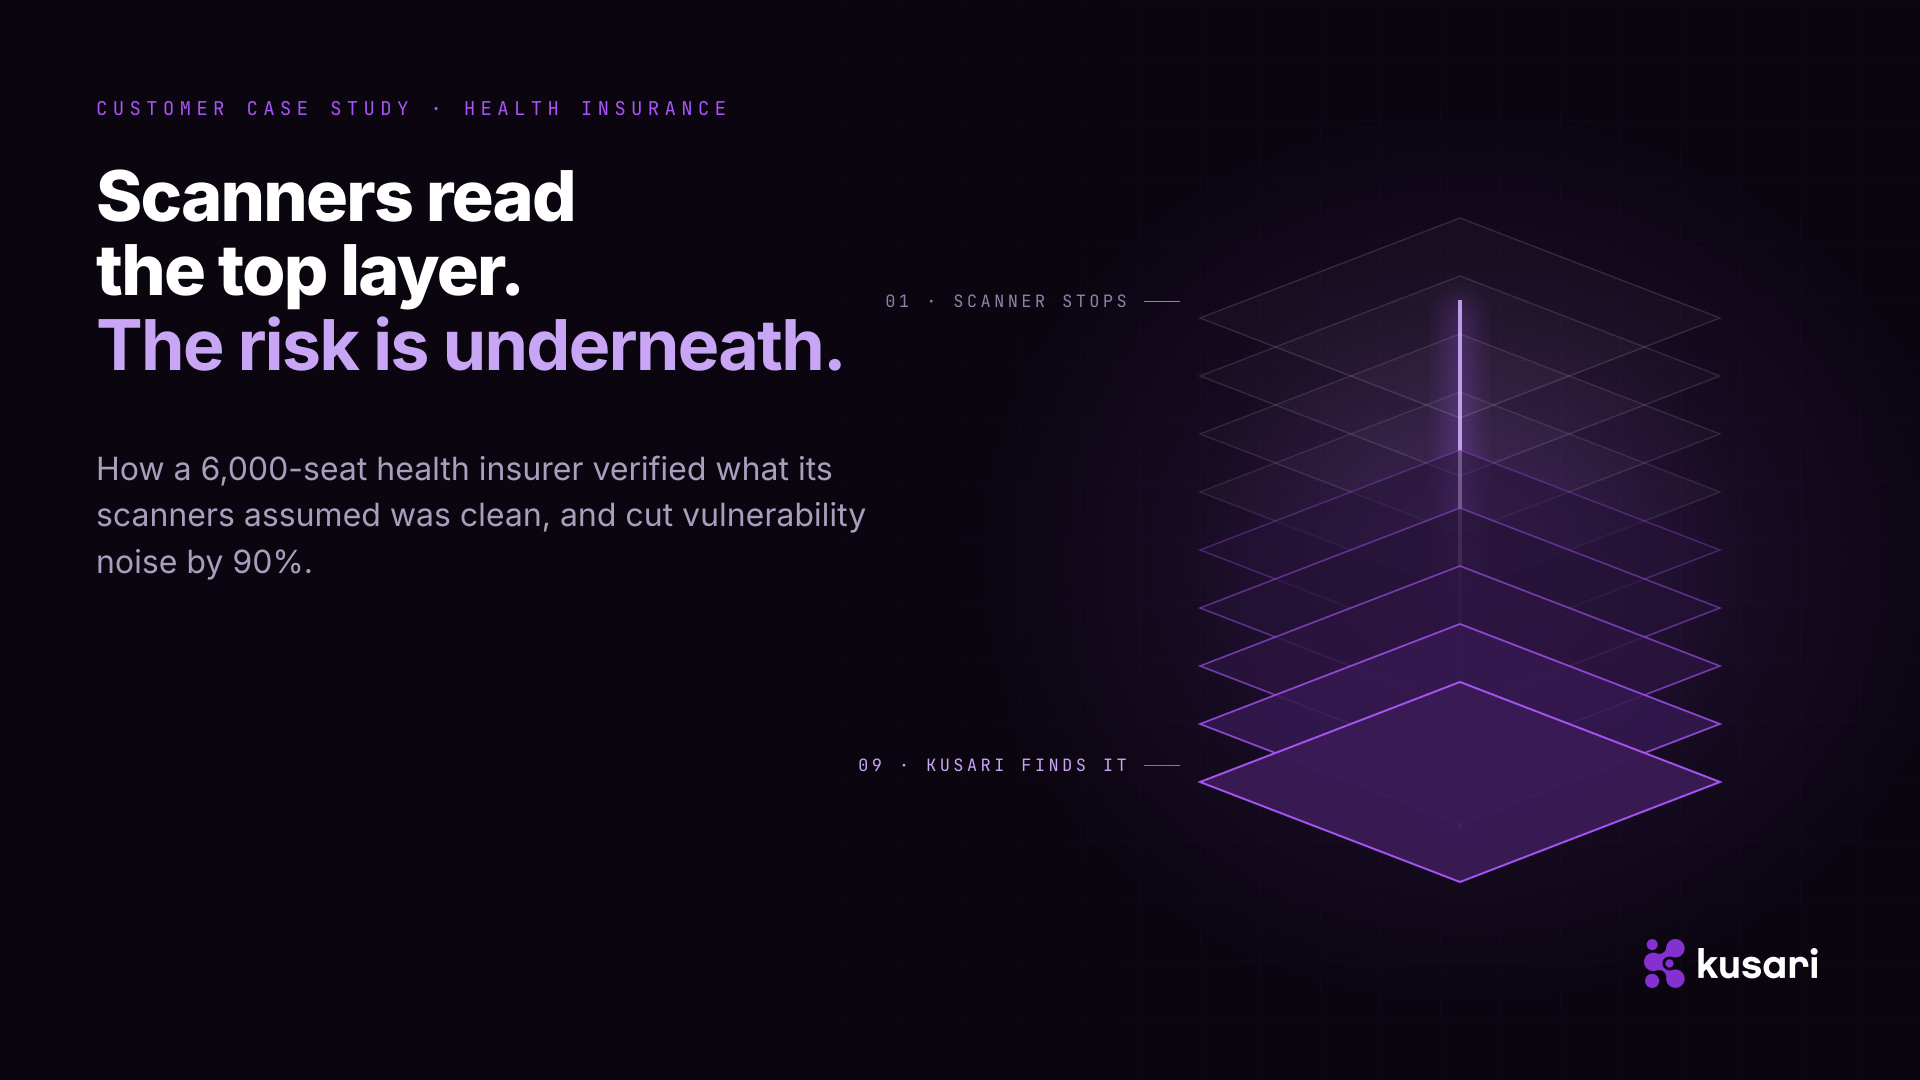
National Health Insurer Transforms Software Supply Chain Security with Kusari
A nonprofit health payer with every scanner in place still couldn't say whether it ran the compromised Axios versions. Kusari answered in minutes — three artifacts, with proof — then stripped 90% of vulnerability noise out of a backlog tens of thousands deep.
Read case study
The AI Vulnerability Storm: A CISO Threat Briefing
Get the executive briefing on the AI vulnerability storm: what changed, why scanners can't keep up, and how to build a Mythos-ready program before the CRA deadline.
Read paper
Coffee With Kusari
A video series of conversations on software supply chain security — featuring founders, maintainers, and practitioners from across the open source community.
Watch
AppSec in Practice Research Report
Research report exploring application security and software supply chain challenges: lack of visibility into vulnerabilities and dependencies, complexity, and difficulties with tool integration.
Read paper
More Trust, Less Boo! Haunt-Free Deployments with Cloudsmith & Kusari
Don't let hidden threats slow you down. Discover how Cloudsmith & Kusari enable proactive security to prevent tampering throughout the software supply chain.
Watch
Medical Device Cybersecurity & FDA 524B Compliance
Ensure medical device cybersecurity, FDA 524B compliance, and SBOM transparency with Kusari. Protect patients, ease legacy device headaches, and streamline pre-market submissions.
Read paper
Seven Critical DevSecOps Strategies for the Software Supply Chain
Key strategies to protect and secure software across the development lifecycle.
Read paper
Open Source Project Security Baseline: Navigate Standards & Regulations
Discover practical strategies to apply the OSPS Baseline to boost your project's security, enhance compliance, and build long-term resilience.
Watch
Securing the Software Supply Chain
Master software supply chain security with our comprehensive guide. Learn best practices from experts to protect your development ecosystem effectively.
Read paper
Five Strategies to Reduce Risk in Your Software Supply Chain
Fortify your software ecosystem against today's sophisticated threats by addressing first-party and third-party risk with equal rigor.
Read paper
CNCF Cloud Native Live: GUAC Use Cases
GUAC use cases beyond security.
Watch
CNCF Cloud Native Live: GUAC 101
Dip into the delicious world of software supply chain security with an introduction to GUAC.
Watch
OpenSSF Tech Talk: Proactive Supply Chain Security with GUAC
An OpenSSF Tech Talk on using GUAC to take a proactive approach to software supply chain security.
Watch